SIEM+ Now Officially Supports Microsoft Sentinel
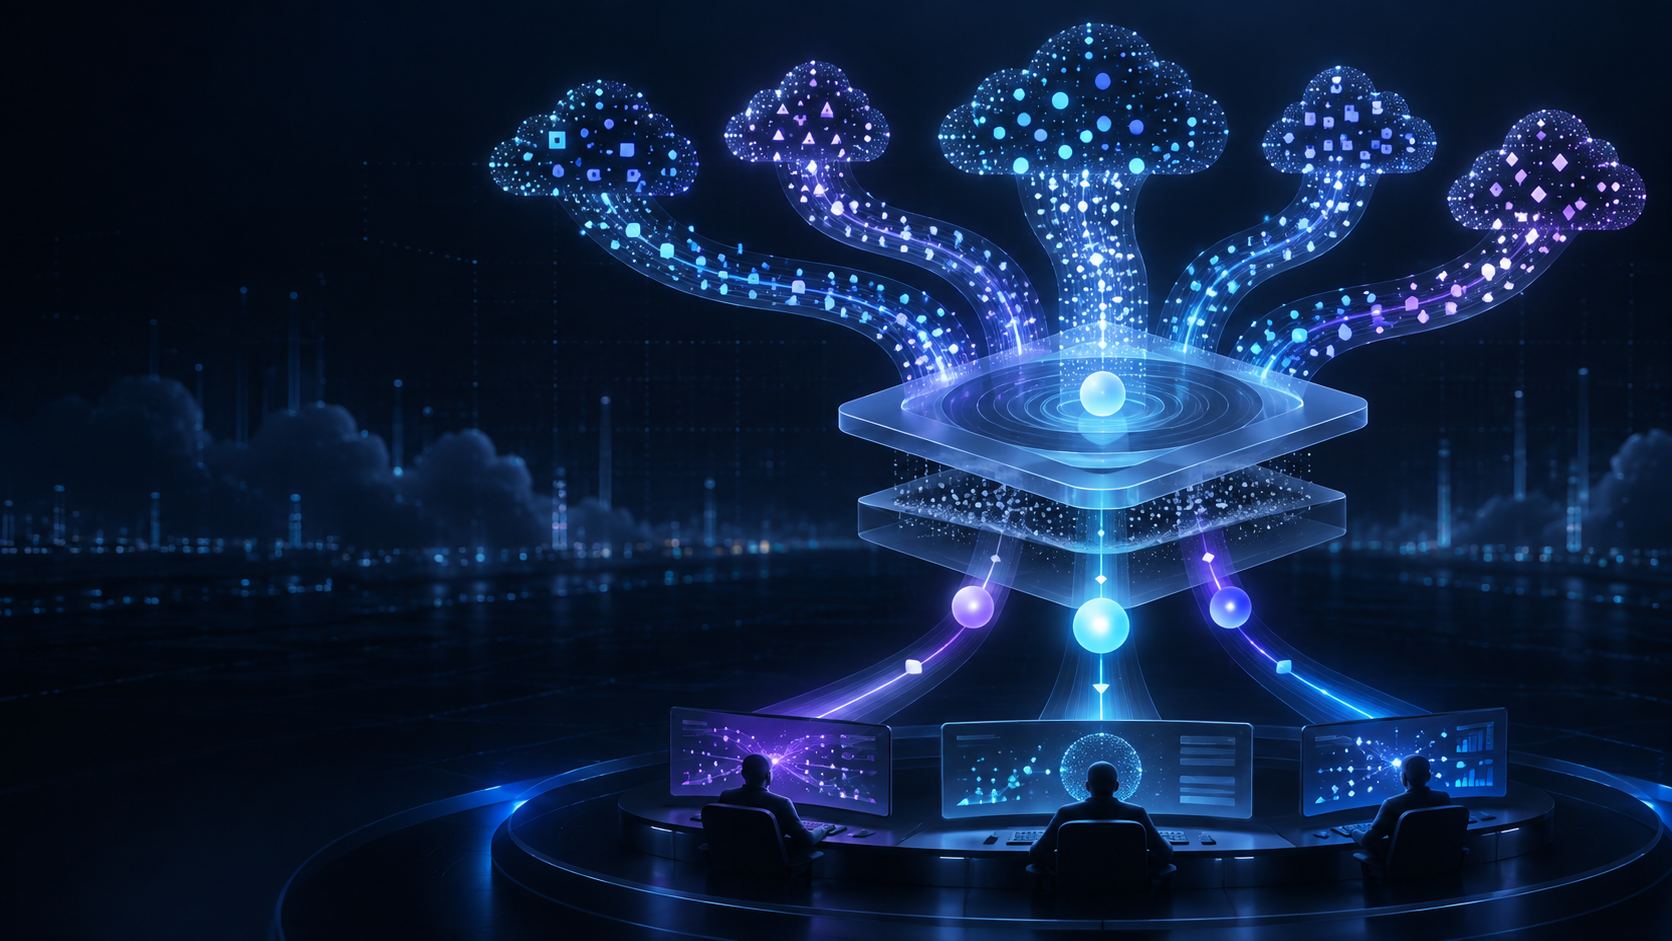
We're announcing that SIEM+ now has full, native support for Microsoft Sentinel, joining our existing integrations with Devo, Splunk, and QRadar. If your organization runs Sentinel as its SIEM, you can now add SIEM+'s alert consolidation and AI-powered triage on top of it without changing anything about your existing Sentinel deployment.
What this means in practice
SIEM+ was built on a simple premise: most organizations don't need another SIEM. They need a better way to see across the one or more they already have.
Adding Sentinel to our supported platforms means:
- Sentinel alerts flow into SIEM+ alongside any other SIEM you run. If you're managing Sentinel in one business unit and Splunk, QRadar, or Devo in another, SIEM+ now gives you a single consolidated view across all of them instead of forcing analysts to switch between consoles.
- AI-driven correlation and noise reduction apply to Sentinel data the same way they do for our other integrations. Duplicate and low-priority alerts get suppressed, and what's left gets translated into plain-English summaries with remediation guidance, so analysts spend less time interpreting raw alert data and more time acting on it.
- No changes are required to your existing Sentinel setup. SIEM+ sits on top of Sentinel as an overlay. Your detection rules, data connectors, and retention policies stay exactly as they are.
Why this integration matters now
Sentinel has become one of the most widely deployed cloud SIEMs, and a growing share of our enterprise conversations—particularly in financial services, pharma, semiconductor, and manufacturing—involve organizations running Sentinel in at least part of their environment. Often, it operates alongside other platforms inherited through M&A or regional IT autonomy.
For these organizations, official Sentinel support means SIEM+ can now serve as a true cross-platform consolidation layer, regardless of which combination of Sentinel, Devo, Splunk, or QRadar makes up their actual environment.
That's the scenario SIEM+ was designed for from the start: reducing alert noise and unifying visibility without forcing a SIEM migration to get there.
How to get started
Sentinel support is available now across all three ways SIEM+ is delivered:
- Standalone overlay — add SIEM+ on top of your existing Sentinel deployment.
- Bundled with Devo — for organizations running Sentinel alongside a Devo environment.
- Managed service — SIEM+ operated on your behalf, spanning Sentinel and any other SIEM in your stack.
If you're already running Sentinel and dealing with alert volume that's outpacing your team's ability to triage it, this is a good time to talk. Reach out to see what a consolidated view across your environment looks like.