SIEM+ Adds Alicloud Security Center and Goes Multi-SIEM for Cross-SIEM Analysis
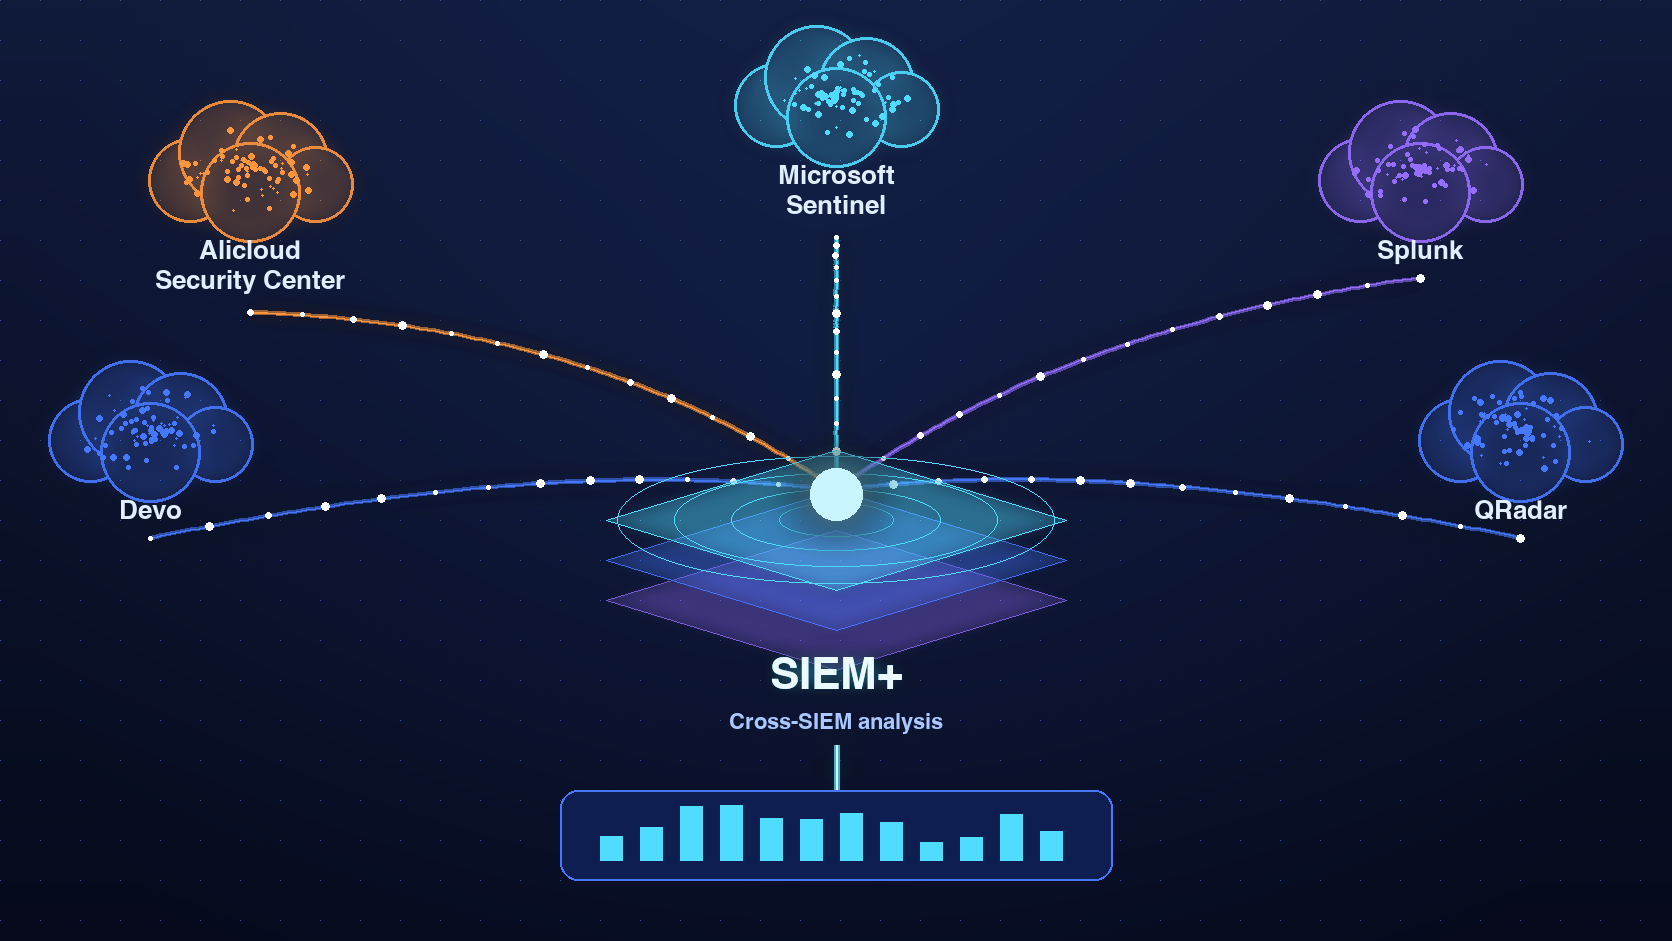
SIEM+ now supports Alicloud Security Center. More importantly, this release lets SIEM+ connect to several SIEM platforms at the same time, so analysts can investigate across them instead of inside one console at a time.
Why Alicloud Security Center
Many of the organizations we work with across Hong Kong, Japan, and Southeast Asia run workloads on Alicloud, often next to Microsoft Azure, AWS, or on-premises systems. Alicloud Security Center is where threat detection, vulnerability, baseline, and cloud workload alerts for those environments come together. Until now, those alerts lived apart from the rest of the security picture.
With this release, Alicloud Security Center joins the platforms SIEM+ already supports: Microsoft Sentinel, Devo, Splunk, and QRadar.
From one SIEM to many
SIEM+ started as an overlay on a single SIEM. This release makes multi-SIEM a first-class capability: you can connect more than one platform to the same SIEM+ workspace and treat them as one source of truth.
That matters because few organizations have one SIEM in practice. A regional business unit may be on Alicloud Security Center, headquarters on Sentinel, and an acquired company on Splunk or QRadar. Each tool sees only its own slice, and attackers don't respect those boundaries.
What cross-SIEM analysis gives you
- One alert queue. Alerts from every connected SIEM are normalized and consolidated, so analysts triage in one place instead of switching consoles.
- Cross-platform correlation. Related activity is linked even when it surfaces in different systems, for example a suspicious sign-in seen in Sentinel followed by unusual behavior on an Alicloud workload.
- Shared noise reduction. Duplicate and low-priority alerts are suppressed across all sources, not just within each one.
- Plain-English cases. The same AI-powered summaries and remediation guidance apply to Alicloud Security Center alerts as to every other integration.
- No rip-and-replace. Your detection rules, connectors, and retention in each SIEM stay as they are. SIEM+ sits on top.
Who this helps
- Multi-cloud enterprises that run Alicloud alongside Azure, AWS, or on-premises systems.
- Groups with acquired or regional entities that each standardized on a different SIEM.
- Organizations migrating between SIEMs that need continuous visibility while old and new platforms run in parallel.
- Managed security customers who want one service spanning every SIEM in their stack.
Availability
Alicloud Security Center support and multi-SIEM connectivity are available across all SIEM+ delivery models:
- Standalone overlay on top of your existing SIEMs.
- Bundled with Devo for organizations running Devo alongside other platforms.
- Managed service, operated on your behalf across every connected SIEM.
If your security data is split across more than one SIEM, we'd like to show you what a single cross-SIEM view looks like for your environment. Get in touch to get started.