SIEM+ Links Campaign Groups into One Attack Chain, with ArcSight, QRadar and Splunk Support Coming Soon
Campaigns in SIEM+ already roll related cases into one story. The latest release goes one level up: campaign groups that belong to the same attack are now linked into a single campaign chain. We are also preparing support for three more SIEM platforms, OpenText ArcSight, IBM QRadar and Splunk, which are coming soon.
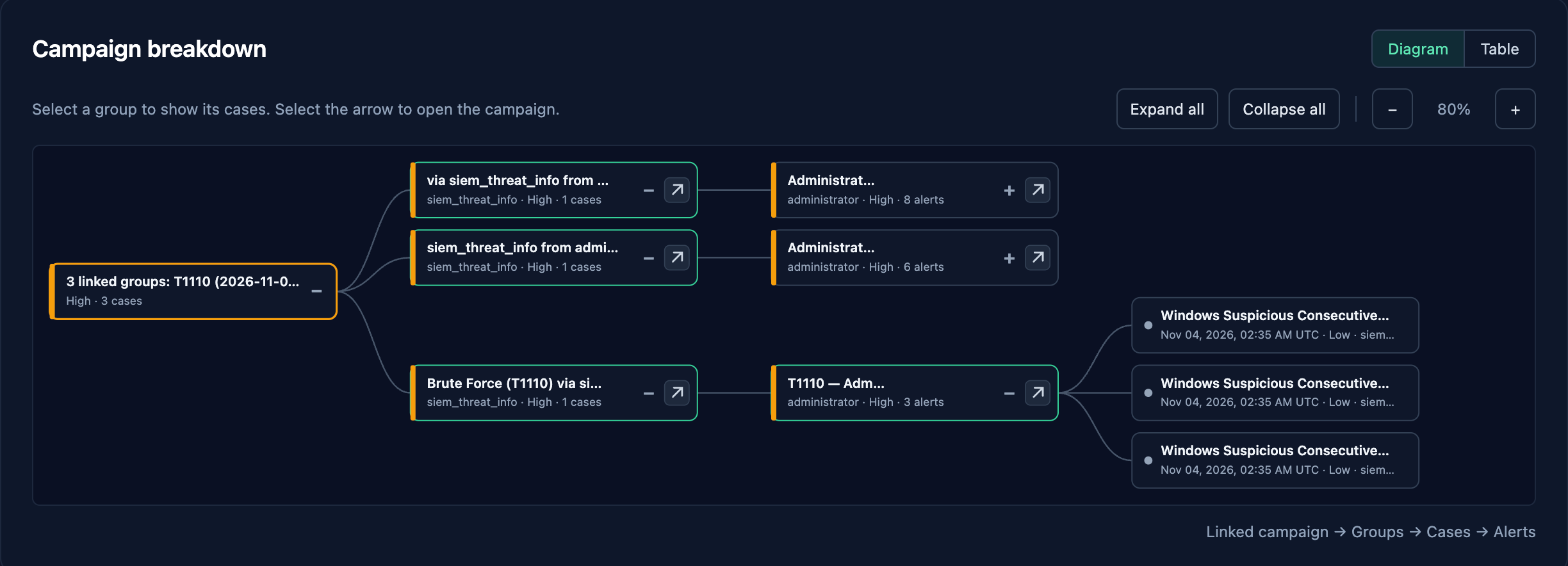
Sample data for illustration.
From cases, to groups, to a chain
The graph above shows how analysts move through the hierarchy:
- Linked campaign: the whole attack story at the top.
- Campaign groups: the rules-based groups that make up the chain.
- Cases: what each group contains.
- Alerts: the evidence behind a single case.
Expand a group to see its cases, and a case to see its alerts. An arrow on each node opens the underlying record.
How groups get linked
Campaign groups that share an identity, an indicator of compromise (IOC) or a target are candidates for a chain. SIEM+ treats the evidence in tiers:
- Strong evidence merges automatically. For example, groups tied together by the same actor identity.
- Borderline pairs go to an AI judge. It proposes a link with a confidence score and a reason code, such as shared actor chain.
- Analysts stay in control. Proposed links stay pending until reviewed, and every merge can be accepted or undone.
Each chain also gets a short narrative with a flow chart and timeline, so a shift handover or an executive summary does not start from scratch.
Verdicts and MITRE review you can audit
A verdict agent assesses cases and campaigns and proposes MITRE ATT&CK mappings. Proposals stay pending until an analyst approves them, and daily security score snapshots track posture over time. The pattern is the same throughout: AI proposes, analysts decide.
ArcSight, QRadar and Splunk: coming soon
SIEM+ officially supports Microsoft Sentinel, Devo and LogEase today, with AliCloud Security Center integration available. Fortinet FortiManager and AWS Security Hub are also on the way.
We are now adding OpenText ArcSight, IBM QRadar and Splunk to that list. Many organizations in Asia run one of them, often next to a newer SIEM, and want AI alert triage, campaign grouping and remediation guidance without replacing what they have. Your detection rules and retention stay in your SIEM; SIEM+ sits on top.
All three integrations are coming soon. If you run ArcSight, QRadar or Splunk and would like early access, get in touch.