
7 posts tagged with "SIEM Plus"

View All Tags

Why Static Dashboards Are Dead: Engineering the Dynamic Posture Score in SIEM+
· 4 min read
James Yip
Managing Director

In the cybersecurity industry, we have a terrible habit of equating “volume” with “risk.” If a traditional SIEM dashboard shows 10,000 alerts, the status indicator turns red, the posture score plummets to zero, and executives panic.

But as any Tier-1 SOC analyst knows, a simple automated port scan against a public-facing IP can generate 5,000 raw firewall drops in three minutes. That isn’t 5,000 separate critical threats; it is a single, low-level event.

When we built SIEM+ (siem.plus), we knew that if we just fed raw alert counts into a UI, we would be recreating the exact same “alert fatigue” we set out to destroy. We needed a way to translate noisy data lakes into a boardroom-ready metric that reflects actual risk.

Here is a deep dive into how we engineered the SIEM+ Dynamic Posture Score, our penalty decay algorithm, and how we force LLMs to map threats to compliance frameworks without hallucinating.
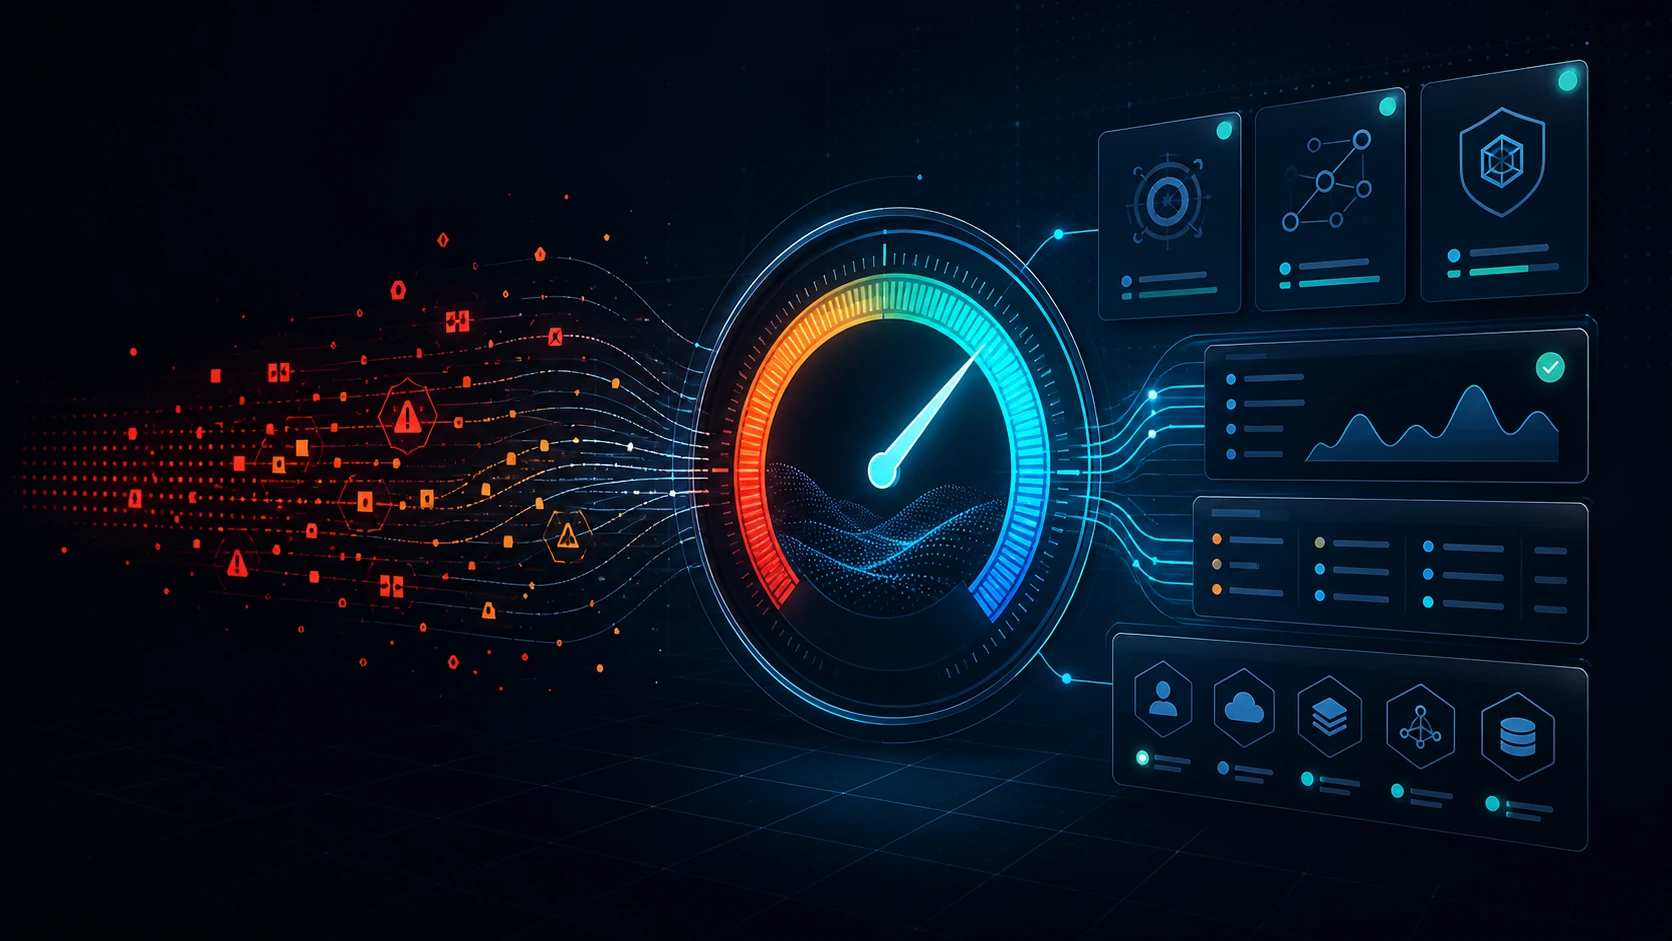
SIEM+ Dynamic Posture Score visualizing grouped cases and actionable risk

SIEM+ Managed SIEM: Cloud-Native Devo Security Monitoring | Eventus

· 6 min read
James Yip
Managing Director

For IT Directors, CISOs, and Security Operations Managers, the challenge is no longer whether the organization has enough security tools. The real challenge is whether a lean team can turn thousands of daily signals into the few decisions that truly matter.

Modern environments generate alerts from firewalls, endpoints, identity platforms, Microsoft 365, cloud workloads, SaaS applications, and network infrastructure. Many of those alerts are low-fidelity. Some are duplicates. Some are known false positives. A small number may indicate real business risk.

This is where SIEM Plus from Eventus comes in. SIEM Plus combines Devo's cloud-native SIEM with Eventus managed services, AI-enhanced noise reduction, and actionable ITSM workflows to help teams conquer alert fatigue without building a large internal SOC from scratch.